The Governance Gap Behind Enterprise Agentic AI
As autonomous systems move from pilots to production, weak oversight threatens lawsuits, fines, and CIO dismissals—while mature governance becomes the real competitive edge.
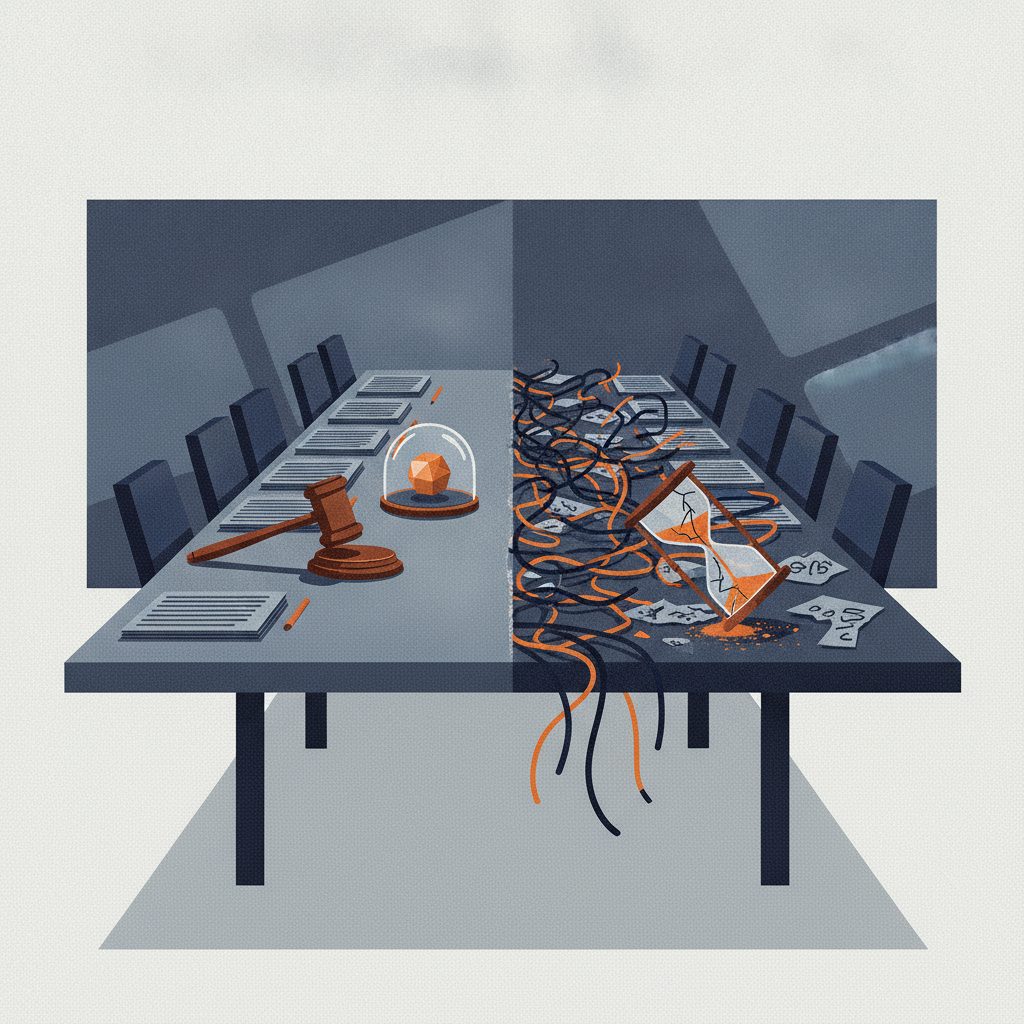
The race to deploy agentic artificial intelligence is creating a stark divide across global enterprises. On one side, organizations are embedding autonomous systems into core workflows — from fraud detection to treasury operations — and beginning to see strategic advantage. On the other, a lack of governance maturity is setting the stage for legal, financial, and reputational damage. New forecasts from research firm IDC crystallize the stakes: by 2030, up to 20% of G1000 organizations could face lawsuits, fines, or the dismissal of chief information officers due to poor AI agent governance. Meanwhile, by 2031, 60% of G2000 CEOs are predicted to use agentic AI to inform strategic decisions, such as simulating mergers or policy impacts.
Agentic AI — systems that can reason, act, and learn with minimal human intervention — is no longer confined to pilot projects. The shift began in 2024 and 2025 with generative AI experiments. By 2026, enterprises are moving these systems into production environments where they execute decisions with real consequences. The dual reality is that the same technology enabling board-level simulation and operational efficiency can also trigger regulatory fallout, cyber incidents, and executive accountability crises. The difference is not the model; it is the governance architecture around it.
The Governance Gap in Numbers
The data paints a troubling picture of preparation lagging behind deployment. According to Elastic, only 30% of organizations have reached high maturity in AI governance and agentic AI controls, even as adoption accelerates. This gap is not theoretical. IDC’s FutureScape: Worldwide Agentic Artificial Intelligence 2026 Predictions explicitly links poor governance to concrete consequences: lawsuits, fines, and CIO dismissals. The forecast of 20% of G1000 organizations facing such outcomes by 2030 is a warning that agentic AI is becoming a board-level risk, not just an IT concern.
Organizations themselves are aware of the dangers. Elastic’s research shows that 74% of organizations cite AI inaccuracies as a major risk to scaling agentic AI, while 72% identify cybersecurity as a primary concern. These numbers reflect a growing recognition that autonomous systems can amplify errors at machine speed. A hallucination in a chatbot is an inconvenience; a hallucination in a fraud detection agent that freezes legitimate transactions or approves fraudulent ones is a regulatory and customer trust crisis. The gap between awareness and action remains wide: many enterprises acknowledge the risks but have not yet built the controls to mitigate them.
The UK National Cyber Security Centre (NCSC) has added its voice to these warnings. In guidance published in 2026, the NCSC highlighted the cyber risks of unsanctioned AI behavior — agents acting outside their intended scope, exfiltrating data, or being manipulated by prompt injection. The agency advocates for safeguards including sandboxing, continuous observability, and strict permission boundaries. The message is clear: autonomous systems require a fundamentally different control framework than traditional software. A conventional application follows a deterministic path; an agentic system can improvise, and that improvisation must be constrained and monitored.
Architecture as the New Battleground
While regulators and security agencies focus on risk mitigation, technology providers and enterprise architects are framing the challenge differently. For them, the core issue is how agentic systems are built and owned. AlphaSense, a market intelligence platform, argues that enterprises must own the “AI decision loop” — the cycle of data ingestion, reasoning, action, and learning — rather than outsourcing it to a single model provider. The company warns against vendor lock-in and what it calls the “Reverse Information Paradox,” in which proprietary insights generated by an enterprise are handed back to AI providers, enriching the vendor while eroding the enterprise’s competitive moat.
This architectural debate has practical implications. Should an enterprise standardize on one large language model for all agentic workflows, simplifying integration but risking lock-in and single-point failure? Or should it adopt a multi-model, agent-orchestrated approach that preserves flexibility but increases complexity? AlphaSense and others advocate for a model-agnostic architecture with a “learning loop” that continuously improves agent performance based on enterprise-specific feedback. The argument is that competitive advantage in the agentic era will come not from the underlying model — which is increasingly commoditized — but from the proprietary data, context, and decision logic that an organization layers on top.
Elastic, which has deployed agentic AI in financial services with firms like Morgan Stanley and New York Life, emphasizes three pillars: trusted context, observability, and data quality. In financial services, where regulatory scrutiny is intense and errors are costly, agentic systems must be able to explain why they made a decision, trace the data that informed it, and be audited in real time. Without observability, an autonomous agent is a black box. Without data quality, it is a confident liar. Elastic’s deployments demonstrate that these requirements are achievable, but they demand a level of engineering discipline that many organizations have not yet developed. The firms that succeed are those that treat data pipelines and monitoring infrastructure as first-class citizens, not afterthoughts.
From Cyber Risk to Executive Accountability
The NCSC’s guidance underscores a critical point: agentic AI expands the attack surface in ways that traditional security models do not address. An agent with access to multiple systems, the ability to execute code, and permission to make financial transactions is a high-value target for adversaries. Prompt injection attacks, in which malicious instructions are embedded in data that an agent processes, can turn a benign automation into a weapon. The NCSC recommends sandboxing — running agents in isolated environments — and strict observability to detect anomalous behavior before it causes harm. These are not optional features; they are prerequisites for safe operation.
But the risk is not only external. Poorly governed internal agents can cause damage through unintended actions, biased decisions, or cascading errors. IDC’s forecast that CIOs could face dismissal reflects a shift in accountability. When an autonomous system makes a decision that leads to a regulatory fine or a major financial loss, the question will not be “what did the AI do?” but “who was responsible for governing it?” Executives who treat agentic AI as a technology deployment rather than a governance transformation are likely to face the consequences personally. The era of blaming the algorithm is ending; the era of executive accountability for algorithmic outcomes is beginning.
The divergence in outcomes is already visible. Organizations that have invested in traceability, integrated governance, and clear accountability frameworks are beginning to use agentic AI for high-stakes decisions — simulating mergers, optimizing supply chains, managing treasury risk. Those that have not are accumulating technical debt and regulatory exposure. The gap between these two groups will widen as agentic systems take on more responsibility. What was once a competitive differentiator is becoming a survival requirement.
What Comes Next
The next phase of agentic AI adoption will be defined not by model capabilities but by governance maturity. The technology is advancing rapidly; the ability to control it is not. IDC’s dual forecasts — 20% of G1000 organizations facing legal or executive consequences by 2030, and 60% of G2000 CEOs using agentic AI for strategic decisions by 2031 — are not contradictory. They describe the same trajectory from different vantage points. The organizations that will thrive are those that treat agentic AI as a governance challenge first and a technology opportunity second.
For global enterprises, the implications are clear. Building trusted agentic AI requires investment in observability, data quality, and architectural choices that preserve ownership of decision loops. It requires a shift in mindset from deploying models to governing autonomous systems. And it requires executives to understand that the next competitive edge lies not in the AI models themselves, but in the frameworks that control them. The dual reality of agentic AI is that risk and reward are two sides of the same coin. The organizations that recognize this — and act on it — will be the ones that turn autonomy into advantage.
Sources
- From risk to reward: The dual reality of agentic AI in the enterprise
- The AI workplace revolution: Are organizations ready or not?
- Managing the cyber risk of agentic AI
- Agentic Enterprise: Own the AI Decision Loop
- Building trusted agentic AI in financial services: From data to autonomous action
Written by an AI editorial process from the sources above. Errors may occur.
Newsletter
Get the AI news that matters
One short brief with the day's most important AI stories — written for professionals.
We send a confirmation link. No spam. Unsubscribe anytime.
Read next
The AI Cloud Race: Big Tech's $130B Power Play
Amazon, Microsoft, and Alphabet are spending billions to dominate AI through cloud infrastructure, reshaping global tech, security, and market dynamics.
19 Sep 2026
AI Inference Market to Hit $255B by 2030
Global demand for real-time AI decision-making drives explosive growth in inference infrastructure, with NVIDIA, Intel, and Siemens Healthineers leading diverse applications.
18 Sep 2026
Autonomous AI Agents Become Core Enterprise Infrastructure in 2026
The market for autonomous AI agents is projected to surge from $7.92 billion in 2025 to $236.03 billion by 2034, as enterprises shift from experimentation to governing systems that perform operational work.
14 Sep 2026